
Most of the "AI compliance" content floating around was written for Fortune 500 legal teams. It assumes you have a Chief Privacy Officer, an in-house counsel, and a dedicated IT security function. You probably have none of those things — and you're using AI anyway, because it's genuinely useful.
So here's the honest version: a plain-English map of the compliance surface that actually applies to a small or midsize business, ranked by how much it should concern you.
This is not legal advice. If you have a specific compliance concern, talk to a lawyer. This is orientation for a business owner who needs to know where to pay attention.
First, a Useful Frame
"Compliance" in this context means three overlapping things:
- Legal obligations — rules you're required to follow under law or regulation
- Contractual obligations — rules you agreed to follow in a vendor's terms of service
- Liability exposure — situations where you could be sued or fined even if you didn't know the rule existed
Most small businesses only think about the first category. The second and third are where the actual surprises tend to come from.
1. Customer and Consumer Disclosure
The short version: In a growing number of situations, you're required to tell people when they're interacting with AI — and the rules vary significantly by state and sector.
The clearest example is customer-facing chatbots. Since July 1, 2019, California has made it illegal to use a bot online to deceive people about its artificial identity in order to drive a sale or influence a vote; clearly disclosing that it's a bot avoids liability. Maine has a similar rule for chatbots in consumer transactions. If you've deployed an AI chat widget on your website that can initiate or complete a sale, a quick "You're chatting with an automated assistant" disclosure isn't just good practice — in some states it's how you stay on the right side of the law.
Beyond chatbots: if you're in marketing, be careful with AI-generated content in advertising. The FTC treats AI-generated deception like any other deception. Its rule banning fake reviews and testimonials covers reviews that claim to come from someone who doesn't exist, including AI-generated ones. The agency has set aside a case against a company that merely sold an AI writing tool, but it says it will keep pursuing businesses that use AI to deceive consumers.
What there isn't is a blanket rule. There's no general federal requirement to disclose every time AI was involved in your work. The disclosure duties that exist are specific and mostly state or local: bots that interact with consumers, AI used in hiring decisions (New York City and Illinois, for example), and AI-generated political ads in several states, including Michigan and Wisconsin. AI-assisted drafting on its own doesn't trigger one. Whether to tell customers anyway is a trust question, not a legal one, and it's worth deciding how you'll disclose AI use to customers on purpose.
What to do: Add a short disclosure wherever a customer interacts with an AI-powered interface. One sentence is usually enough. Review any AI-generated marketing materials and confirm you're not inadvertently creating false impressions about endorsements or results.
2. Copyright and Ownership of AI Output
The short version: Content generated by AI tools is in murky legal territory, and you should understand the practical risks before you use it commercially.
The U.S. Copyright Office says purely AI-generated material, including output produced from prompts alone, can't be copyrighted, and the courts have upheld its human-authorship requirement. This means if you ask an AI to write a marketing brochure with minimal human editing, you may not actually own that brochure in the traditional legal sense — and more importantly, neither does anyone else, which makes it harder to protect.
The more pressing risk runs in the other direction: AI tools can produce content that infringes on someone else's copyright. This is especially relevant for images and code. Artists and stock-photo companies are suing AI image companies such as Stability AI and Midjourney over training on copyrighted images, and early rulings have gone both ways. Those suits target the AI companies, not their customers. But if an output closely copies a protected work, the business that publishes it could face a claim.
Practically speaking, the risk isn't zero, but it's manageable:
- For images: Favor tools that stand behind their output. Business and enterprise plans from the major AI image tools often include IP indemnity that personal plans don't. Check your plan's terms: coverage usually depends on the plan, the contract and how you use the tool.
- For code: The same goes for AI coding assistants: business and enterprise plans often include IP indemnity that personal plans don't. Check your plan's terms before you rely on it.
- For text: The risk is lower than for images, but don't reproduce large blocks of AI output in contexts where you'd care about attribution or originality (legal filings, published research, etc.).
What to do: Check whether your AI tools carry any IP indemnification. For commercial-use images especially, favor tools with explicit licensed-content training. Register meaningful human-created work that incorporates AI assistance.
3. Vendor Terms and Contracts
The short version: The most binding compliance obligations you have probably came with the Terms of Service you clicked through.
This is the least glamorous compliance category and the one most businesses are actually exposed on.
A few specific things worth checking:
Data input restrictions. Most enterprise AI tools — ChatGPT, Claude, Gemini, Copilot — have terms governing what data you can submit to the model. Submitting confidential client information, protected health information, or employee personal data to a consumer-tier AI tool may violate the tool's terms, and depending on your sector, it may also violate data protection law. The enterprise/business tiers of these tools typically offer data processing agreements (DPAs) that address this. If your team is using AI to process any sensitive customer or employee data, you should be on a business tier with a DPA in place — not a personal account.
State privacy laws. California, Colorado, Virginia and Connecticut all have consumer privacy laws that give residents rights over their personal data. Most apply only above size thresholds: California's, for example, covers businesses with annual revenue in the tens of millions of dollars or data on 100,000 or more consumers. Connecticut's is the exception worth knowing: it also covers businesses that process Connecticut consumers' sensitive data, such as health information, regardless of size. If one of these laws covers you, sending customer data to an AI vendor is generally fine when the vendor is contractually bound to process it only on your behalf. It can count as a "sale" when the vendor can use the data for its own purposes, such as training models for other customers.
Output restrictions. Some tools have restrictions on how you can use AI-generated content commercially. Most of the major ones are fairly permissive for business use, but it's worth confirming — especially for niche or specialized AI tools.
Confidentiality risks in multi-tenant systems. When you feed a vendor's AI system information about your pricing, strategy, or proprietary processes, that data is transmitted to and processed by a third-party system. Understand where it goes, whether it's used for model training, and whether your confidentiality obligations to clients or partners cover this.
What to do: Take 30 minutes to check the terms for the AI tools your team actually uses. Confirm you're on the right tier for business use. If your business handles sensitive client data, talk to your attorney about whether you need a DPA with each AI vendor.
4. Hiring and HR Decisions
The short version: If AI touches who you interview, hire or promote, this is the area where AI-specific rules already reach small employers.
New York City's Local Law 144 requires employers that use automated hiring or promotion tools on NYC candidates to get an independent bias audit within the year before use, post a summary of the results on their website, and notify candidates at least 10 business days ahead.
Since January 1, 2026, Illinois has barred employers from using AI in hiring, promotion, discipline or firing in a way that has a discriminatory effect, and requires them to tell workers when they use AI for those decisions. A separate Illinois law requires notice and consent before AI analyzes a recorded video interview.
Colorado replaced its 2024 AI Act before it took effect. Under the replacement, starting January 1, 2027, employers that use automated decision tools to materially influence hiring decisions must tell applicants beforehand, explain within 30 days any rejection the tool influenced, and, on request, let applicants correct their data and get a human review where that's commercially reasonable.
Even where no AI-specific rule applies, discrimination law still does. If you use a screening tool, the hiring decision is still yours, and so is the legal risk if the tool screens people out unfairly. A vendor's assurance that the tool is unbiased doesn't move that responsibility to the vendor. Federal enforcement against unintentional bias has narrowed, but state laws like Illinois' target discriminatory effects directly.
What to do: If your applicant tracking system scores or ranks candidates, ask the vendor whether the tool has been audited for bias and whether it supports the notice rules where you hire. Keep a person meaningfully in the decision. "AI flagged three candidates and a manager reviewed them" is a very different posture from "AI rejected 400 applications automatically."
5. Sector-Specific Rules: Health, Finance, and Legal
If your business operates in healthcare, financial services, or legal services, the AI compliance picture is materially different — not because new AI-specific laws have passed, but because existing sector regulations already cover the relevant risks, and regulators are actively applying them.
Healthcare
HIPAA applies to healthcare providers, health plans and clearinghouses, and to businesses that handle patient data on their behalf. If you're one of them and protected health information (PHI) goes into an AI tool, the vendor must sign a Business Associate Agreement (BAA) first: a contract HIPAA requires whenever a vendor handles PHI for you. Many consumer AI tools don't offer one. Microsoft (including Copilot under its business terms) and Google Workspace (including Gemini) do offer BAAs for business accounts, but you still have to accept the agreement, stick to the covered services and configure them correctly.
Using a consumer AI tool to draft clinical notes, analyze patient records, or process any identifiable health information without a BAA in place is a HIPAA violation — even if the vendor never actually misuses the data.
Financial Services
FINRA has said plainly that its rules apply when member firms use AI, just as they do with any other technology: supervision, communications, recordkeeping and fair dealing all still apply. The SEC withdrew its proposed AI-specific conflicts rule, but the existing securities laws still apply to AI-assisted advice. If you're an RIA or broker-dealer, AI tools that influence investment recommendations need to be evaluated within your existing compliance framework.
For most small financial services firms, the immediate action is documentation: if AI is touching any client-facing analysis or recommendation, note that in your compliance records and review it for consistency with your existing policies.
Legal Services
The American Bar Association and many state bars have issued guidance on attorney competence obligations as applied to AI — the core question being whether an attorney who uses AI to draft documents meets their duty of competence. The answer is generally "yes, if you review and understand the output." The liability concern isn't using AI; it's using AI output without adequate review. Courts have sanctioned attorneys for filing AI-invented case citations, most famously in Mata v. Avianca (2023), and those cases are the clearest examples of AI-specific professional liability in any field.
If you're at a small law firm, the compliance obligation is really a quality-control obligation: never submit AI-generated legal research or drafting without verifying every material claim.
6. Emerging Regulation: What's Worth a Glance
The EU AI Act is the most comprehensive AI regulation in the world, and it now largely applies: bans on certain practices since February 2025, rules for general-purpose AI models since August 2025 and most other provisions since August 2026, with obligations for high-risk systems pushed back to December 2027 (August 2028 for AI built into regulated products). It can reach a U.S. business that offers AI systems in the EU or uses AI whose output is used there; handling EU residents' personal data is a separate question under the GDPR. For most U.S.-focused SMBs it's background noise. Watch it; don't lose sleep over it.
In the U.S., the AI regulation picture is a patchwork. There's no comprehensive federal AI law. The Biden-era AI executive order was revoked in January 2025, and the Trump administration's orders favor lighter regulation and push back on state AI laws: a December 2025 order set up a Justice Department task force to challenge them. Federal oversight comes mainly from existing laws enforced by agencies like the FTC and from sector regulators, while state AI laws still apply.
Colorado repealed and replaced its first AI Act before it took effect. The replacement, whose duties start January 1, 2027, covers automated decisions about employment, housing, financial services and more, which puts AI in hiring inside the rules. California has enacted AI transparency laws, but they put obligations on the companies that build AI (training-data summaries, labels on AI-generated media), not on small businesses that simply use AI tools.
The honest read: broad federal AI regulation for small businesses isn't close. The compliance risk that's real comes from the existing rules already described — sector regulations, FTC authority, state laws and contractual terms — not from legislation that hasn't passed.
What's Noise vs. What's Worth Acting On
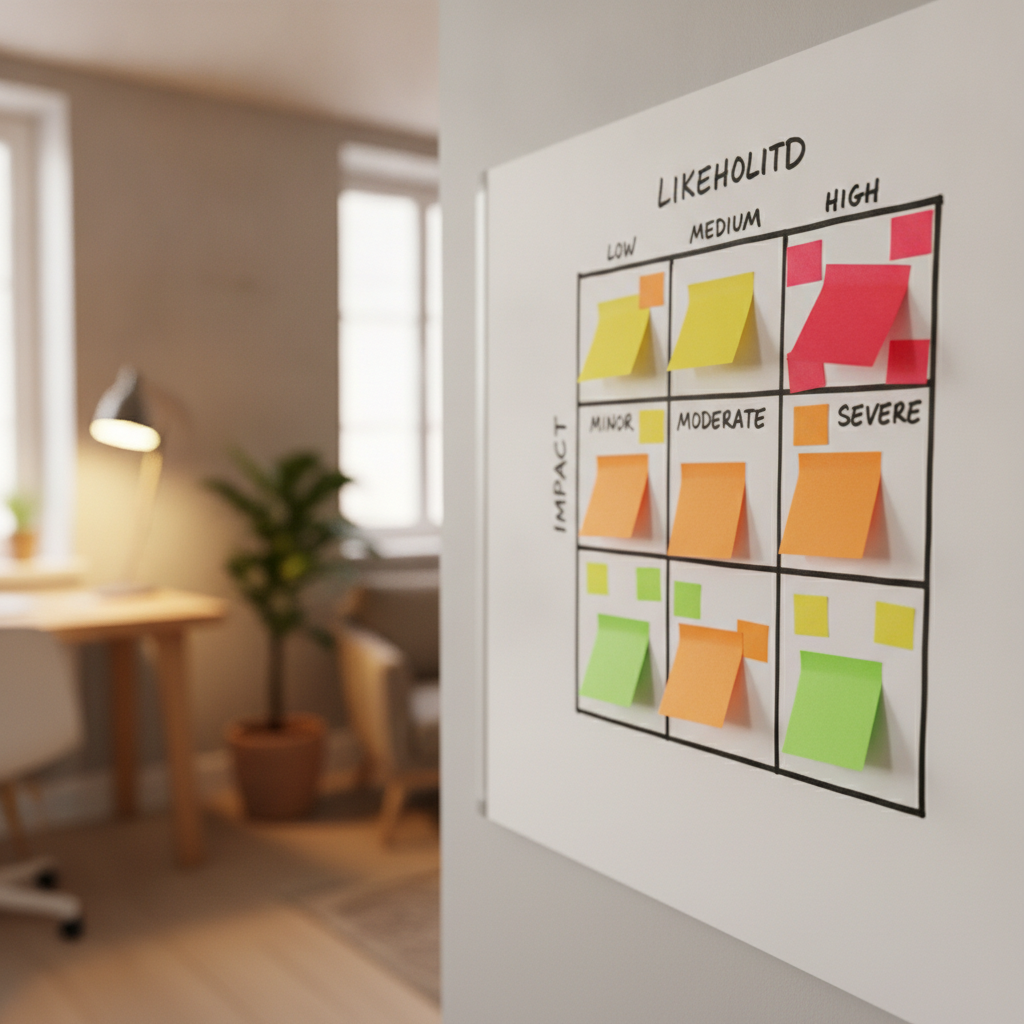
Here's the honest triage:
| Area | Priority | Why |
|---|---|---|
| Vendor terms & data input rules | High — act now | Easy to break without noticing |
| Customer-facing AI disclosure | High — act now | Low effort, real legal exposure in several states |
| HIPAA / BAAs (if healthcare) | High — act now | Existing law, active enforcement |
| AI in hiring (NYC, Illinois, Colorado) | High if you hire there | AI-specific rules: bias audits, notices, human review |
| Copyright on commercial images | Medium | Risk is real but manageable with the right tools |
| Sector rules (finance, legal) | High if applicable | Existing frameworks apply directly |
| EU AI Act | Low for most U.S. SMBs | Monitor, don't act urgently |
| Federal AI legislation | Low | Hasn't passed; watch the space |
The Compliance Posture That Actually Makes Sense for an SMB
You don't need a compliance program. You need a few deliberate decisions, ideally written down in a simple AI policy:
- Know what tools your team is actually using — shadow AI use (employees using personal AI accounts for work tasks) is where most SMB exposure actually lives.
- Match the tool tier to the sensitivity of the data — free consumer tiers for internal brainstorming; enterprise tiers with DPAs for anything touching client or patient data.
- Add one sentence of disclosure wherever customers interact with AI.
- Check your hiring tools if you hire in New York City, Illinois or Colorado: ask the vendor about bias audits and candidate notices.
- Talk to your attorney once — a single 30-minute conversation about your specific sector and state is often enough to close the obvious gaps.
None of this requires a big project. It mostly requires knowing what you have and making a few deliberate choices about how you use it.
This is the kind of risk mapping we walk through with clients — figuring out where an SMB's actual AI exposure is (usually not where they expected) and what a proportionate response looks like. If you want that conversation for your business, book a strategy call and we'll make it useful.